Data Destruction: The Forgotten Link in Cybersecurity
For Cybersecurity Awareness Month, a closer look at how offline data, chain of custody, and NAID AAA certification fit into protecting business information
A laptop can leave the network without leaving behind the sensitive information stored inside it. The same is true of a retired server, a backup tape, or a hard drive sitting in a storage closet.
For organizations reviewing their defenses during Cybersecurity Awareness Month, these offline assets raise a question that deserves attention alongside passwords, phishing, and network protection:
What happens to business data after the equipment holding it goes out of service?
Taking a device offline changes how it can be accessed. It does not, by itself, remove the information it contains. Protecting that information requires a process that continues through storage, collection, transportation, sanitization, and final disposition.
That makes secure data destruction—and the chain of custody leading to it—part of the cybersecurity lifecycle.
Offline Data Remains a Security Responsibility
Offline data is information stored on media that is disconnected from a network or active system. It can reside on retired computers, external drives, solid-state drives, backup tapes, USB devices, and other storage media. Depending on their configuration, printers, copiers, and other connected equipment may also retain information.
Offline storage can serve a legitimate security purpose. Isolated backups, for example, can support recovery planning. The concern is unmanaged media: equipment whose contents, location, access permissions, or intended disposition are unclear.
A device may have little resale value while still holding valuable information—customer records, employee details, financial documents, intellectual property, or credentials. The business may consider the equipment obsolete. Its information still needs protection.
Where Equipment Retirement Creates an Accountability Gap
Retirement often moves equipment across departmental boundaries. IT disconnects devices and updates its inventory. Facilities clears space. Procurement selects a service provider. A collection team removes the equipment.
Without an agreed process connecting those steps, each department can finish its assignment while questions remain about the data.
Consider a hypothetical office relocation. Old laptops are placed in a storage room before pickup. Over several weeks, more devices are added, a few are removed for spare parts, and the original count becomes unreliable. When the collection occurs, a receipt confirms that equipment changed hands. But the organization may no longer be able to establish whether every original device was included.
The vulnerability began before transportation or destruction. It began when inventory and custody stopped matching.
For that reason, equipment awaiting disposition should remain within the organization’s information security controls, with an accountable owner and a defined next step.
What Chain of Custody Means for Data Destruction
A chain of custody documents possession and transfers as equipment moves toward its authorized outcome. For data-bearing assets, the record should connect what the organization released with what the provider received and ultimately sanitized or destroyed.
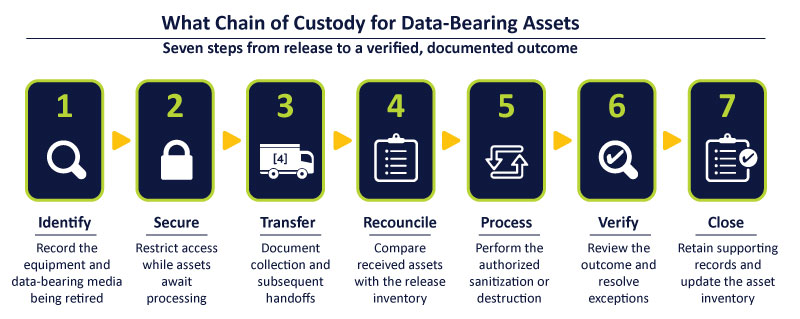
A practical process follows seven steps:
- Identify: Record the equipment and data-bearing media being retired.
- Secure: Restrict access while assets await processing.
- Transfer: Document collection and subsequent handoffs.
- Reconcile: Compare received assets with the release inventory.
- Process: Perform the authorized sanitization or destruction.
- Verify: Review the outcome and resolve exceptions.
- Close: Retain supporting records and update the asset inventory.
The tracking method should suit the assets and risk. Individually managed devices may require asset-level or media-level identifiers. Other approved processes may use controlled batches.
In either case, discrepancies need attention. A missing drive or an unsuccessful sanitization attempt should trigger a documented response.
How NAID AAA Certification Supports Vendor Due Diligence
NAID AAA Certification®, administered by i-SIGMA, provides independent assessment of information destruction providers. The program includes scheduled and unannounced audits, with scrutiny of safeguards such as secure processes, chain of custody, and employee background screening. That gives customers evidence to consider when evaluating a provider’s operations.
Organizations should verify the provider’s current certification and confirm that its scope covers the proposed service, location, and media. i-SIGMA maintains separate certification applications for physical media destruction and electronic media erasure.
Certification supports vendor due diligence. It works alongside the customer’s own responsibilities: defining the work, controlling assets before collection, and reconciling the completed service.
Secure Data Destruction and Media Sanitization
Physical destruction is one possible outcome for retired storage media. Equipment intended for reuse may instead undergo an appropriate sanitization process, subject to the organization’s security requirements.
NIST’s Guidelines for Media Sanitization, SP 800-88 Revision 2, addresses the establishment of a sanitization program with methods and controls appropriate to the sensitivity of the information. Published in September 2025, it supersedes Revision 1.
That program approach matters because the decision should be made before equipment enters a disposal stream. Organizations need to establish what the media may contain, whether reuse is authorized, which process is appropriate, and how the outcome will be verified. They also need instructions for equipment that cannot be processed successfully.
A file deletion, a device marked “retired,” or a collection receipt should not be treated as evidence that those requirements have been satisfied.
Why a Certificate of Destruction Needs Supporting Records
A certificate of destruction is an important closing document. Its value depends on how clearly it connects to the work performed.
If an organization releases an inventory of data-bearing assets, the final documentation should allow it to reconcile those assets with the applicable outcomes and identify unresolved exceptions. Useful records may include identifiers, quantities, processing dates, methods, results, and references connecting collection records to final documentation.
The central question is simple: Can the organization account for the media it released and demonstrate that it reached an authorized outcome?
A pickup establishes that a transfer occurred. Reconciliation and final documentation establish whether the process is complete.
A Cybersecurity Awareness Month Check for Retired Equipment
October’s Cybersecurity Awareness Month provides an opportunity to examine this part of information security. Organizations can start with five questions:
- Where is retired data-bearing equipment currently stored?
- Who can access it, and who owns the retirement process?
- Does the inventory reflect the equipment and storage media actually present?
- Has the provider’s current certification and relevant service scope been verified?
- Can completed collections be reconciled with sanitization or destruction records?
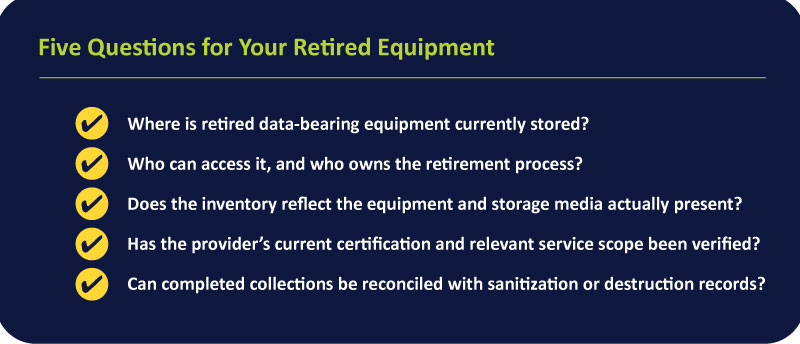
These questions can bring IT, security, facilities, and procurement into the same conversation before the next equipment refresh or office move.
Cybersecurity Continues After the Last Login
A complete cybersecurity strategy follows information throughout its lifecycle, including the period when equipment is disconnected and awaiting disposition. Secure storage, documented handoffs, qualified providers, and verified outcomes help maintain that continuity.
For business leaders, the lesson is clear: taking equipment out of service should begin a controlled retirement process. Responsibility for its information continues until that process is complete.
---------------
Planning an equipment refresh, office move, or storage cleanout? Contact 4THBIN to discuss secure data destruction and responsible IT asset disposition.